Edit this page on GitHub (opens in a new tab)
A zk-SNARK is a short proof that a statement is true. Anyone can check it quickly, and it reveals nothing except that the statement holds. Zcash uses these proofs so the network can verify a shielded transaction without seeing who sent it, who received it or how much it moved.
Say you claim to have solved a very hard Sudoku. You could show the filled grid, but then the checker learns your solution and can copy it. A zero-knowledge proof is like handing the checker a short receipt that convinces them a valid solution exists, while the grid itself stays hidden.
Real proofs are mathematics, not paper, but the idea is the same. The Zcash network is the checker, and the "solution" is the private data of your transaction.
When you send shielded ZEC, your wallet builds a proof on your device and attaches it to the transaction. Every node checks the proof, and it convinces them that:
The nodes learn none of the underlying details. The proof is not encryption: the contents of a payment, including its memo, are encrypted separately for the recipient.
| Pool | Proof system | Trusted setup |
|---|---|---|
| Sprout | BCTV14 at launch, Groth16 later | Yes, from a 2016 ceremony |
| Sapling | Groth16 | Yes, from a multi-party ceremony |
| Orchard | Halo 2 | No |
| Ironwood | Uses the Orchard protocol (ZIP 258) | See the page |
A trusted setup produces secret randomness that must be destroyed. If someone kept it, they could forge proofs, which means creating coins out of nothing. It would not reveal anyone's private data. Halo 2 removed that dependency, which is the main reason Orchard was built on it. Sprout is a legacy pool; see and for the older designs.
No trusted setup does not mean no bugs. In May 2026 researchers found a missing constraint in the Orchard circuit (CVE-2026-54496) that could in theory let a dishonest prover forge a proof. fixed it, and no evidence of exploitation has been reported. later made Orchard spend-only. In July 2026 zkSecurity published an audit of the fixed Orchard code (orchard 0.14.0 and halo2_gadgets 0.5.0), commissioned by the Tachyon Foundation. Its report states that its findings do not affect the security of the deployed Orchard protocol. The page has the full timeline.
| Common belief | What is actually the case |
|---|---|
| "A zk-SNARK makes every Zcash transaction private." | The proof protects shielded transactions. A transaction that touches a transparent address still reveals those parts. |
| "All Zcash pools use the same proofs." | Sprout began with BCTV14, Sapling uses Groth16 and Orchard uses Halo 2. |
| "No trusted setup means the system cannot have bugs." | It removes one risk only. The 2026 Orchard circuit bug shows circuits can still have flaws. |
| "The proof is what hides my payment." | The proof shows validity. The payment contents are hidden by encryption and by the note design. |
| "A zero-knowledge proof can be reversed to recover the data." | It is built so that it reveals nothing beyond the truth of the statement. |
The sections below cover the theory behind the proofs. You do not need them to use Zcash.
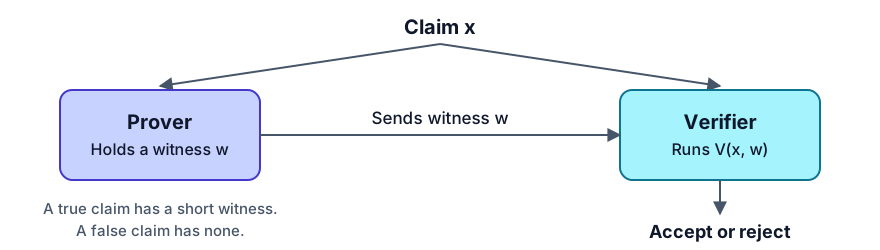
A proof is a claim together with a sequence of steps that lets anyone confirm the claim is true. Mathematics works this way: the fact that the angles of a triangle add up to 180 degrees can be checked independently by anyone, who plays the role of the verifier. In cryptography both the prover and the verifier are algorithms.
Computer science calls proofs that can be checked efficiently NP proofs. The idea is that a solution exists, and the prover hands it over for the verifier to check in polynomial time. A proof system of this kind has two properties:
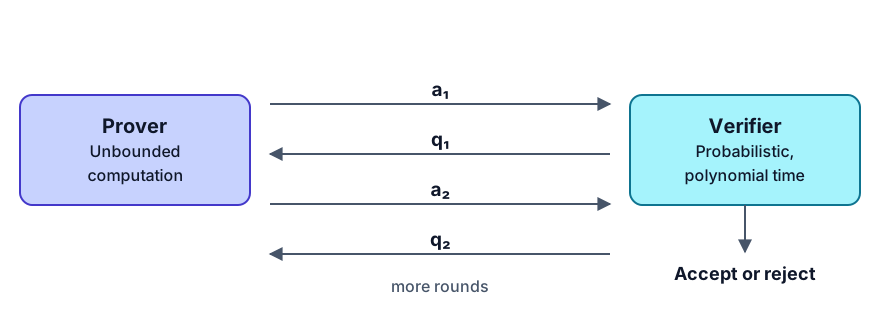
Instead of reading a single proof, the verifier can talk to the prover over several rounds. The verifier's questions are random, so the prover has to be able to answer every possible question correctly. With interaction and randomness together, a verifier that runs only in probabilistic polynomial time can be convinced of claims that a single NP proof could not efficiently establish.
| Statement type | Meaning | One NP proof | Interactive proof |
|---|---|---|---|
| NP | A solution exists | Yes | Yes |
| co-NP | No solution exists | Not believed to be possible | Yes |
| #P | Counting how many solutions exist | Not believed to be possible | Yes |
| PSPACE | Alternating statements | Not believed to be possible | Yes |
A protocol is zero knowledge if the verifier learns nothing from the interaction beyond the fact that the claim is true. What the verifier could compute afterwards, they could already compute before: the rounds of messages did not increase their power.
Cryptographers formalize this with a simulator, an algorithm that does not know the secret but can still produce transcripts that look like a real conversation between prover and verifier. The two views, real and simulated, are computationally indistinguishable if no efficient algorithm that is given many samples can tell them apart better than guessing. In other words, its chance of picking the right one stays at 1/2, plus an amount too small to matter.
Interactive protocols are most useful when there is a single verifier, such as a tax auditor in a zero-knowledge proof of taxes.
A SNARK is a Succinct Non-Interactive Argument of Knowledge: a short proof that a statement is true, fast to verify, and sent in a single message from the prover to the verifier, who then accepts or rejects. A zk-SNARK adds zero knowledge, so the proof reveals nothing about the secret data.
For example, the statement "I know a message m such that SHA256(m) equals a given value" can be proved without revealing m.
A SNARK starts by turning the statement into a polynomial problem. A polynomial is a sum of terms made of constants, variables and exponents of variables, such as 3x² + 8x + 17. The computation itself is written as an arithmetic circuit: a directed acyclic graph in which each node performs an addition or a multiplication, the way a boolean circuit carries bits on its wires but with numbers instead.
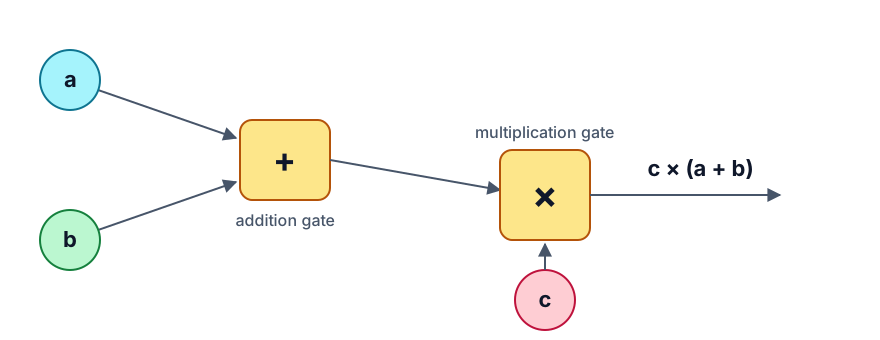
In this example the prover wants to convince the verifier that they know values for a, b and c that satisfy the circuit.
A setup procedure helps the verifier by summarizing a circuit and producing public parameters. There are three kinds:
| Setup | How it works | Examples |
|---|---|---|
| Trusted setup per circuit | Run once for each circuit. The secret randomness (the common reference string) must be kept secret and destroyed. If someone keeps it, a dishonest prover can prove false statements. | Groth16 |
| Trusted but universal setup | The trusted setup runs only once, and can then be used to preprocess many circuits. | Sonic, Marlin, PLONK |
| Transparent setup (no trusted setup) | The preprocessing uses no secret randomness at all. | DARK, , |
Groth16 has very short proofs that can be verified quickly, but needs a trusted setup. The transparent systems avoid a trusted setup at the cost of slightly longer proofs or a prover that may take longer to run.
SNARKs are useful when many verifiers need to check the same proof, as on a blockchain such as Zcash: the validating nodes do not have to interact with the prover over several rounds for every proof.
Zero-knowledge proofs enforce honest behavior in a protocol without revealing any information. Zcash is a public blockchain, so every node must be able to check the rules. The proofs let nodes check that a private transaction follows the consensus rules without learning anything else about it.
Video Explainer: in this lecture Ariel Gabizon describes the Zcash note commitment tree, blind polynomial evaluation and homomorphically hidden challenges, and how they are implemented on the network.
Read the Halo 2 book for more information.